


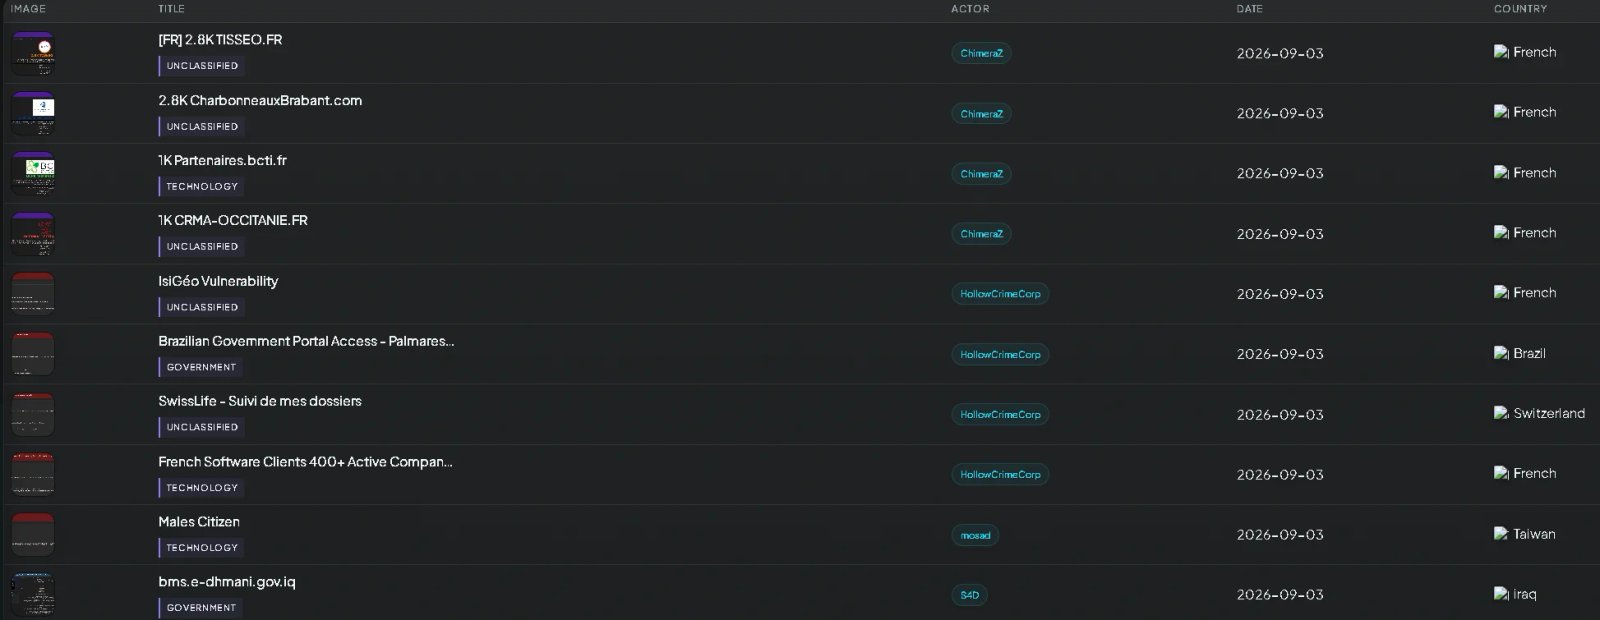
Threat Intelligence Alert: New Victims in the Crosshairs
The cybersecurity community is on high alert after the detection of a new batch of posts in cybercrime ecosystems pointing to France, Brazil, Switzerland, Taiwan, and Iraq as potential targets. According to threat intelligence (CTI) sources, the reports indicate activity related to data leaks, access sales, database exposure, and targeted attacks on government and private-sector entities.
The status of this information is UNCONFIRMED, meaning that although the signs are concerning, the magnitude or authenticity of the compromised data has not yet been officially verified. However, the mere existence of these posts on clandestine forums and dark web markets justifies a thorough investigation by incident response teams in the affected countries.
What are cybercrime ecosystems?
Cybercrime ecosystems are complex networks of forums, markets, and encrypted communication channels where malicious actors exchange tools, stolen data, and illegal services. These spaces operate on the dark web and the deep web, and are the breeding ground for activities such as ransomware, identity theft, and corporate espionage.
Types of threats detected
The CTI report classifies the threats into several categories, each with different implications for victims:
- Data Leak: Unauthorized publication of confidential information, which may include personal data of citizens, trade secrets, or internal communications.
- Access Sale: Commercialization of credentials to computer systems, corporate networks, or privileged accounts, often obtained through phishing or malware.
- Database Exposure: Complete databases that are exposed or stolen, containing massive records of users, clients, or employees.
- Government / Private-Sector Targeting: Targeted attacks on government infrastructures or private companies, for espionage, sabotage, or economic gain.
Countries named and possible implications
The alert mentions five countries across three continents, suggesting a global operation or coordinated attacks by different groups:
| Country | Possible affected sector | Potential risk |
|---|---|---|
| France 🇫🇷 | Government / Private sector | Espionage, theft of personal data |
| Brazil 🇧🇷 | Government / Private sector | Financial fraud, identity theft |
| Switzerland 🇨🇭 | Government / Private sector | Leak of banking or corporate information |
| Taiwan 🇹🇼 | Government / Private sector | Cyberespionage, attacks on critical infrastructures |
| Iraq 🇮🇶 | Government / Private sector | Destabilization, data theft |
Recommendations for organizations and users
In the face of such alerts, experts recommend taking proactive measures to mitigate risks:
- Continuous monitoring: Regularly review access logs and suspicious activities in systems.
- Multi-factor authentication (MFA): Implement MFA on all critical accounts to hinder unauthorized access.
- Software updates: Keep security patches up to date to close known vulnerabilities.
- Incident response plan: Have a clear plan to act quickly in case of a security breach.
Threat Intelligence (CTI) is a discipline that collects and analyzes information about potential attacks to anticipate them. This alert is a reminder that cybersecurity is a shared responsibility among governments, companies, and citizens.
We will keep this news under follow-up and update the information as facts are confirmed or new details emerge.