


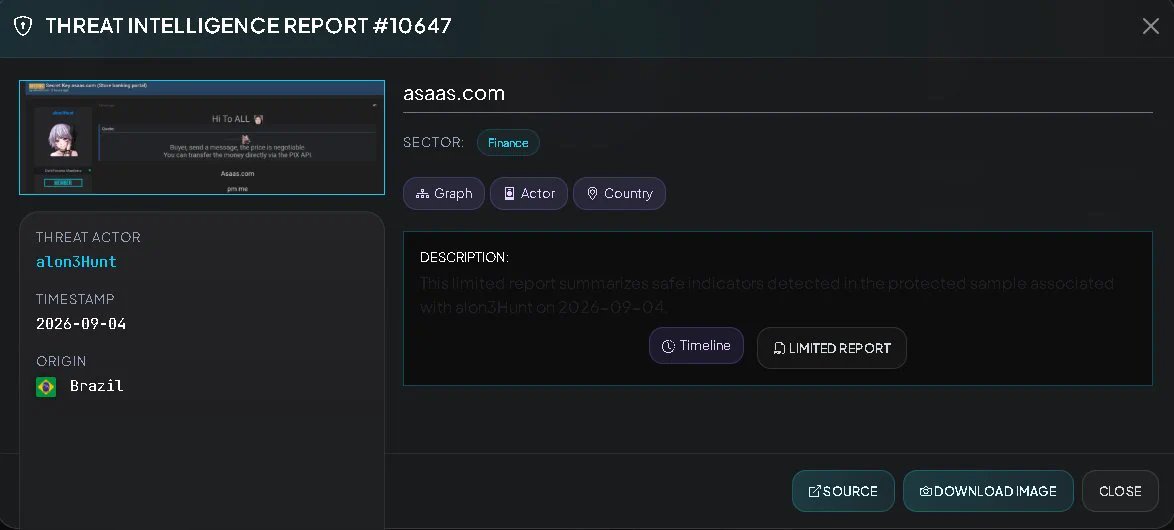
The threat intelligence team CTI Alert has detected a post on the clandestine forum DarkForums where the actor identified as alon3Hunt claims to have obtained a secret API key linked to Asaas, one of the most used payment and financial management platforms in Brazil. The post, classified as unconfirmed, suggests that the exposed key could grant access to financial operations and enable fraudulent transfers through the PIX system.
Asaas is a Brazilian fintech that offers collection, payment, and cash flow management solutions for small and medium-sized businesses. Its integration with the PIX system, the instant payment method created by the Central Bank of Brazil, makes it an attractive target for cybercriminals seeking to divert funds quickly and hard to trace.
What does an API key leak mean?
An API key (Application Programming Interface key) is an authentication code that allows software to communicate with another securely. In the context of Asaas, an exposed API key could allow an attacker to perform operations such as:
- Check balances and movements of linked accounts.
- Initiate unauthorized PIX transfers.
- Modify beneficiary data or payment settings.
- Access sensitive information of the fintech's clients.
Although the DarkForums post has not been independently verified, the mere fact that a possible active key has been disseminated generates real risk, especially if it was obtained through phishing, malware, or a breach in the company's systems.
The context of threats to fintechs in Brazil
Brazil is one of the countries with the highest adoption of digital payments in the world, and the PIX system, launched in November 2020, processes billions of transactions per year. This popularity has also attracted cybercriminals, who constantly seek vulnerabilities in financial platforms to commit fraud.
Cases like Asaas are not isolated. In recent years, similar incidents have been reported in other Brazilian fintechs, which has led the Central Bank to strengthen security requirements and companies to invest in multi-factor authentication and real-time transaction monitoring.
Recommendations for users and companies
While waiting for official confirmation from Asaas or Brazilian authorities, cybersecurity experts recommend to users and companies that use the platform:
- Immediately review the activity logs of their accounts for unrecognized movements.
- Change passwords and enable two-factor authentication (2FA).
- If API integrations are used, regenerate keys and limit permissions to the minimum necessary.
- Stay alert to official communications from Asaas about the incident.
Credential leakage is one of the main causes of financial fraud in the region, and the exposure of an API key with access to PIX operations could have serious consequences if not mitigated in time.
What is known so far?
According to the CTI Alert report, the post on DarkForums was made by the user alon3Hunt, who did not provide conclusive evidence of the key's validity. The status of the incident is unconfirmed, and there is no public evidence that fraudulent transfers have been made so far.
Asaas has not issued an official statement on the matter as of this writing. Users are recommended to follow the company's official channels for updated information and avoid spreading rumors without verifiable basis.
This case underscores the importance of cybersecurity in the fintech ecosystem and the need for both companies and users to adopt proactive measures to protect their data and money.